Posting on behalf of the site owner, a UK registered charity.
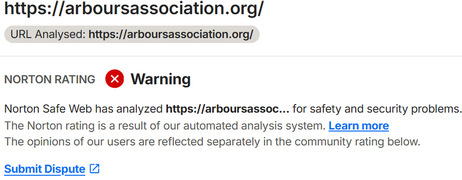
arboursassociation a dot org tld was genuinely compromised on 12 June 2026 with an injected JavaScript loader (a blockchain-hosted ClickFix campaign). I am the site’s developer and I remediated it fully on 31 August 2026, removing a rogue plugin, a must-use plugin dropin, a concealed backup archive in the uploads directory, and an injected entry in the database. Credentials were rotated, salts regenerated, WordPress and all plugins updated, and the suspected entry vector removed.
This was not a false positive — the original detection was correct — and I am not disputing it. I am asking for a rescan now that the site is clean.
Current status:
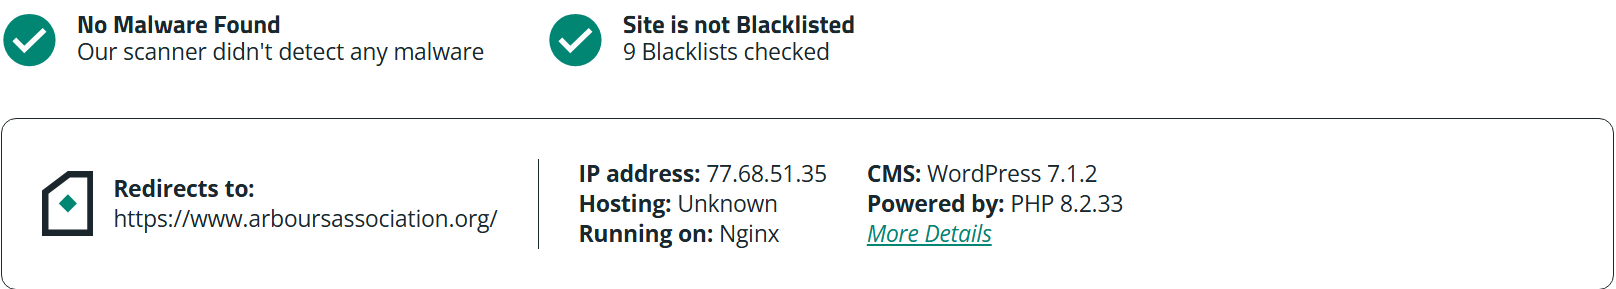
Sucuri SiteCheck: clean, low risk
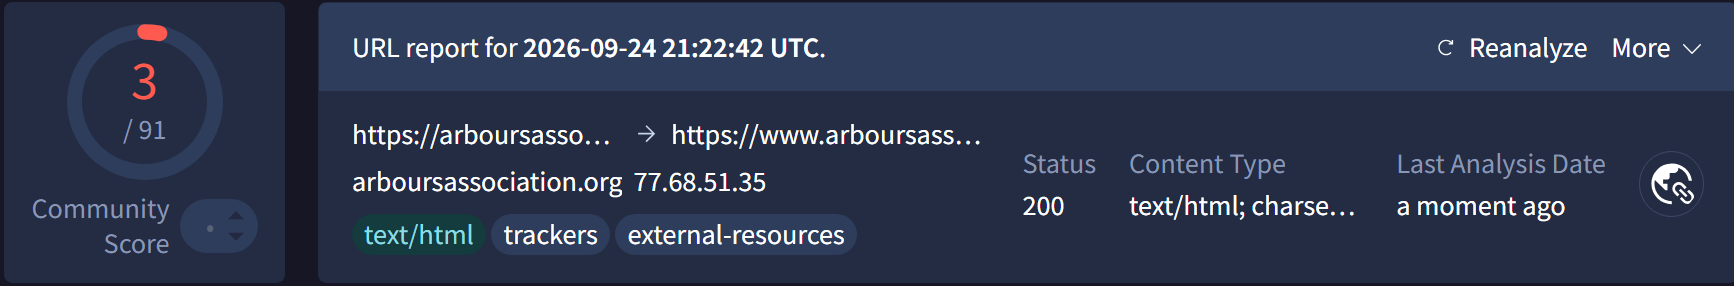
VirusTotal: scanned 7 hours ago; the server IP (77.68.51.35) is clean across all 91 vendors
Direct inspection confirms no injected code on any page
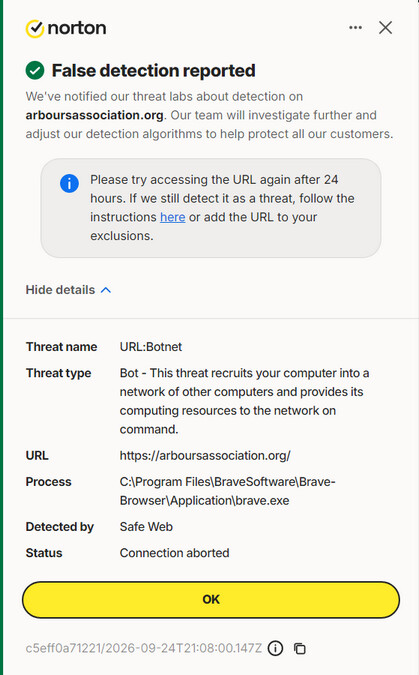
Detection name: URL:Botnet
Remediated: 31 August 2026
Submitted via the false positive form
Norton Safe Web ownership: verified
Could someone perform a manual review and clear the outdated entry?
Thanks