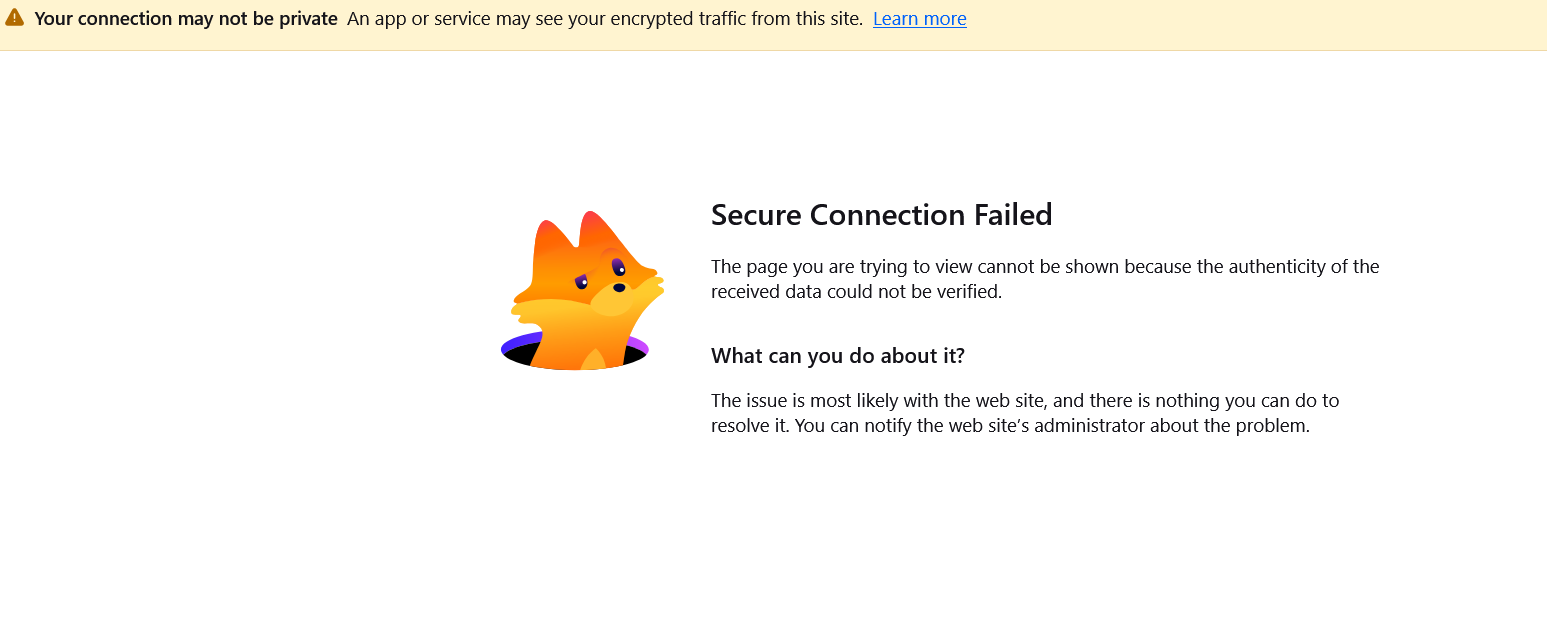
“Your connection may not be private” from Firefox

Here is some general AI generated information about what you are seeing:

AI Overview

If Firefox is warning you about SSLKEYLOGFILE being enabled on your system, it means that Norton antivirus or security software is intercepting and decrypting your browser’s secure HTTPS traffic to scan it for threats. [1]

SSLKEYLOGFILE is a standard environment variable recognized by Firefox and Chrome. When it is active, the browser automatically dumps its underlying SSL/TLS encryption keys into a specified log file. Antivirus programs leverage this built-in capability to see the raw text of encrypted websites, ensuring no malware, scams, or phishing scripts are sneaking past the secure connection. [1, 2, 3]


Is it safe to leave enabled?

  • Yes, if you trust Norton: It is safe if you trust Norton to act as the intermediate monitor for everything you do online. It is a legitimate method used by many security tools to perform HTTPS scanning / Web protection. [1]

  • The Caveats: Having your browser dump encryption keys means that any software running on your computer with access to that log file could potentially decrypt and inspect your traffic. Furthermore, intercepting connections this way can occasionally cause connection errors, broken pages, or security warnings inside Firefox. [1]

POSSIBLE solution:

AI Overview

To stop Norton from using or triggering the SSLKEYLOGFILE environment variable/behavior in Firefox, you need to disable Norton’s HTTPS/Encrypted Web Scanning feature or remove the environment variable set on your system. [1, 2]

Step 1: Disable HTTPS Scanning in Norton

Norton injects or reads the SSLKEYLOGFILE variable to inspect secure traffic, which can trigger warnings or errors in Firefox. [1]

  1. Open your Norton 360 app or antivirus interface.

  2. Click on Settings (or go to Security and look for advanced settings depending on your version).

  3. Select Firewall or Web Protection.

  4. Look for Encrypted Web Scan or HTTPS Scanning.

  5. Toggle the switch to OFF.

  6. Apply or save the changes. [1, 2, 3]

Step 2: Remove the System Environment Variable (If Manually Set)

If an SSLKEYLOGFILE variable was explicitly created in Windows for your user account or system:

  1. Press the Windows key, type env, and select Edit environment variables for your account.

  2. In the Environment Variables window, look under User variables and System variables for a variable named SSLKEYLOGFILE.

  3. If it exists, select SSLKEYLOGFILE and click Delete.

  4. Click OK to save and close all windows. [1, 2]

Step 3: Restart Firefox

  1. Close Firefox completely. Make sure no background processes are running by checking the Windows Task Manager.

  2. Relaunch Firefox for the changes to take effect. [1, 2]

  • Explore troubleshooting details from Mozilla Support regarding TLS key logging and network warnings.

SA
Indeed; much of that was tried (and again now, same results). Disabling components of Norton doesn’t seem to prevent the variable from being set (Security > Advanced Security, and disabling a load of stuff there). In fact I’m seeing it get set in all browsers, even Norton’s own Private Browser.

Trouble is there’s conflicting reports about whether Norton sets this variable or not. Their own A.I. agent says Norton doesn’t set it, their phone technical support seemed to suggest it had something to do with the ISP, but other avenues seem to be suggesting it’s being set by Norton. So I’m not sure if it’s malware that’s setting it or not, and getting all the decrypted traffic. Done a full scan and nothing’s showing up. Going to see what MalwareBytes has to say about things.

Thanks for responding though. If anyone else has any thoughts/contributions do chime in

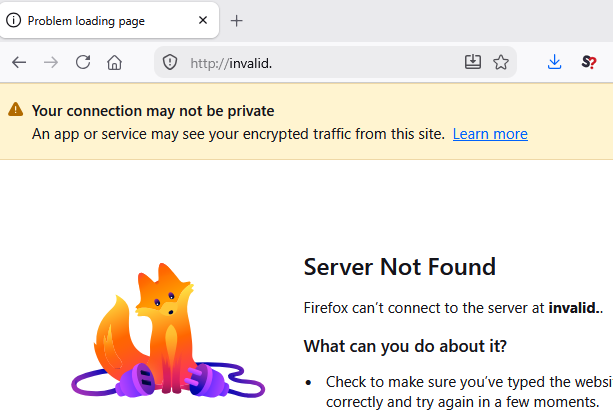
Also, screenshot of Firefox’s warning message. Only seems to display if Firefox can’t connect to somewhere, and SSLKEYLOGFILE is set. The URL in the screenshot is guaranteed to never connect anywhere, so is a good way of testing to see if the warning is coming up or not; be interesting to hear if other Norton users are also getting this warning. From the date of the article it links to, it looks like this warning might be relatively new.

I get similar (below), I’m using a new Asus Vivobook laptop that I’m getting various annoying issues with that I don’t get on my older Asus laptop (screen broken), I’m getting this error inconsistently with other similar issues like website not loading 1st time (and then does 2nd or 3rd time), I get similar issues with other browsers so I don’t believe it’s a browser dependant problem. AI seems to suggest it’s a Norton issue but I have Norton 360 installed on my broken Asus laptop and I don’t get the same issue, I’m using Windows 11 on both. It’s flippin’ annoying !

Please note that I used a translation tool, so some wording may sound unnatural.

My Situation

After viewing a thread in the Norton Community, I checked my own systems.

On my PC, when I checked about:support in Firefox around 19:00 JST on September 2, 2026, SSLKEYLOGFILE = \\.\nllMonFltProxy\<random alphanumeric string> was displayed. When I completely closed and restarted Firefox, the alphanumeric string at the end changed. The entry did not disappear even when I paused Safe Web; a value of the same format remained visible even after briefly stopping Auto-Protect and the Firewall and disabling the Norton extension. Furthermore, even after restarting Windows and checking immediately upon startup, the same \\.\nllMonFltProxy\<random alphanumeric string> was displayed.

I could not find SSLKEYLOGFILE in the Windows user or system environment variables. On my father’s Windows 10 PC, there was likewise no SSLKEYLOGFILE in the persistent environment variables, yet Firefox showed a value of the same format, with the ending changing upon every restart. However, in my checks, SSLKEYLOGFILE did not appear in the environment variables for Thunderbird.

Around 4:00 AM on September 3, 2026, when launching Firefox and accessing Yahoo!, I encountered a connection failure screen stating “Server not found.” At the top, a warning appeared stating: “Your connection is not private. An app or service may be able to see your encrypted communications with this site.”

This warning also appeared when in Airplane Mode resulting in an NS_ERROR_OFFLINE error. However, back on July 13, 2026, while NS_ERROR_OFFLINE would appear in Airplane Mode, I do not recall seeing this specific warning.

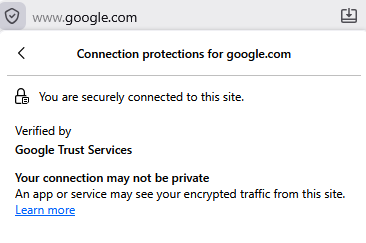
Additionally, even on standard web pages, when I opened the connection information to the left of the address bar and viewed the “Connection is secure” status, a warning of the same type appeared below the Certificate Authority field. Hovering the cursor over “More information” revealed a link to sslkeylogfile-warning, and clicking it took me to the Mozilla Support page in Japanese. As part of the safety verification, the offline scan completed successfully with zero threats detected, and the full scan also found no threats requiring resolution.

Below is my hypothesis, separated from the observations above for clarity.

My Hypothesis

Norton’s official support documentation states that the software sometimes uses its own certificates to inspect encrypted web content, which can trigger related messages in Firefox. This suggests that Norton is designed to be deeply involved in the inspection of HTTPS traffic.

Additionally, previous information from support indicated that hostnames such as gen-webserver.local, redirector.gen-webserver.local, and revocation.gen-webserver.local are used for traffic interception and inspection by a local web server, Safe Web routing, and certificate revocation checks. Combining this information with the SSLKEYLOGFILE = \\.\nllMonFltProxy\<random alphanumeric string> entry and the “Your connection is not private” warning observed in Firefox, it seems likely that Norton’s web protection and HTTPS inspection mechanisms are involved.

Based on these findings, the issue appears to be a behavior common to multiple environments rather than an isolated infection. In particular, since the value does not exist in Windows’ persistent environment variables yet reappears after restarting Firefox or Windows and was observed on other PCs as well, it seems to be generated dynamically upon Firefox startup rather than being a static manual configuration.

Furthermore, while Mozilla’s article on sslkeylogfile-warning primarily discusses the large warning displayed on network error pages, I observed a similar warning within the connection information panel of standard web pages in my environment; the embedded link referenced firefox/155.0. I had not seen this specific warning in that location prior to Firefox 155.0, so I believe it began appearing with version 155.0 or later. However, I cannot yet determine whether this stems from a change in Firefox 155.0 itself or results from an interaction with a Norton update released around the same time.

Chronologically, on July 13, 2026, only the NS_ERROR_OFFLINE screen appeared, whereas by September 3, 2026, the “not private” warning was displayed alongside the connection failure message. Furthermore, following a Norton patch update on August 19, 2026, at 00:24, entries in the hosts file shifted from the .local domain to the .internal domain. Given this, along with a report from user Reciprocal in late August 2026 noting the recent appearance of Firefox SSLKEYLOGFILE warnings, I suspect that changes related to Norton’s web traffic handling or HTTPS inspection are likely involved. However, I have yet to receive an explanation from Norton Support regarding why the switch from .local to .internal occurred.

In short, my current assessment is that it is more likely that nllMonFltProxy-related displays and warnings are surfacing due to the interaction between Norton and Firefox, rather than this being a case of individual system infections.

Yeah I can confirm occassional connectivity problems with sites too, such as “Content-Encoding Error”, which then disappear upon refresh. Was originally how I encountered the “Your connection may not be private” warning in fact. Has only been happening in recent months.

Amazing; thanks for all this. This would strongly suggest that an SSLKEYLOGFILE of \\.\nllMonFltProxy\… is from Norton and not malware. I’ve run whole system scans with Norton and MalwareBytes as well and neither detected anything.

Also, can confirm upon updating to Firefox 155 this warning has been made more prominent; I’m now seeing the following too—


The timescales mentioned appear to match when the “Your connection may not be private” warning was supposedly implemented in Firefox; the article it links to suggests Firefox started warning about SSLKEYLOGFILE from mid–late June 2026.

Interesting disabling various Norton features doesn’t disable the setting of SSLKEYLOGFILE, something I’ve observed too, which is what had me worried if it was genuine.

Regarding the change of use from the .local TLD to the .internal TLD, I’d say this is likely a result of standardization efforts, and unrelated. The .local TLD is meant for use with mDNS, though has often been misused for regular DNS services running on the local computer/network. IETF have been promoting the use of the .internal TLD for such uses over the past couple of years.